II Cyber Warfare & Critical Infrastructure·Analysis·Europe
The invisible front: subsea cables, zero-day vulnerabilities and 153 million identity documents
Three incidents that came to light in a single week show the threat to critical infrastructure growing simultaneously across the physical, software and data layers.
Cyber & Critical Infrastructure Desk · 12 September 2026 · 8 min read · 5 sources
Why it matters
A sabotage rehearsal targeting the Svalbard cables, the BlueMoon exploit kit rapidly shared by China-aligned groups and the theft of 153 million driving licence scans show different actors targeting the same weakness: the dependence of critical services on a small number of physical links and suppliers.
Implications
- Because satellite data infrastructure depends on a few cables on the seabed, a single act of sabotage could disrupt it on a regional scale.
- Zero-day vulnerabilities being shared among state-linked groups within a few days effectively eliminates the window between patch and exploitation.
- The concentration of identity verification services in a single supplier means one breach can affect millions of people in two countries.
Physical layer: cables
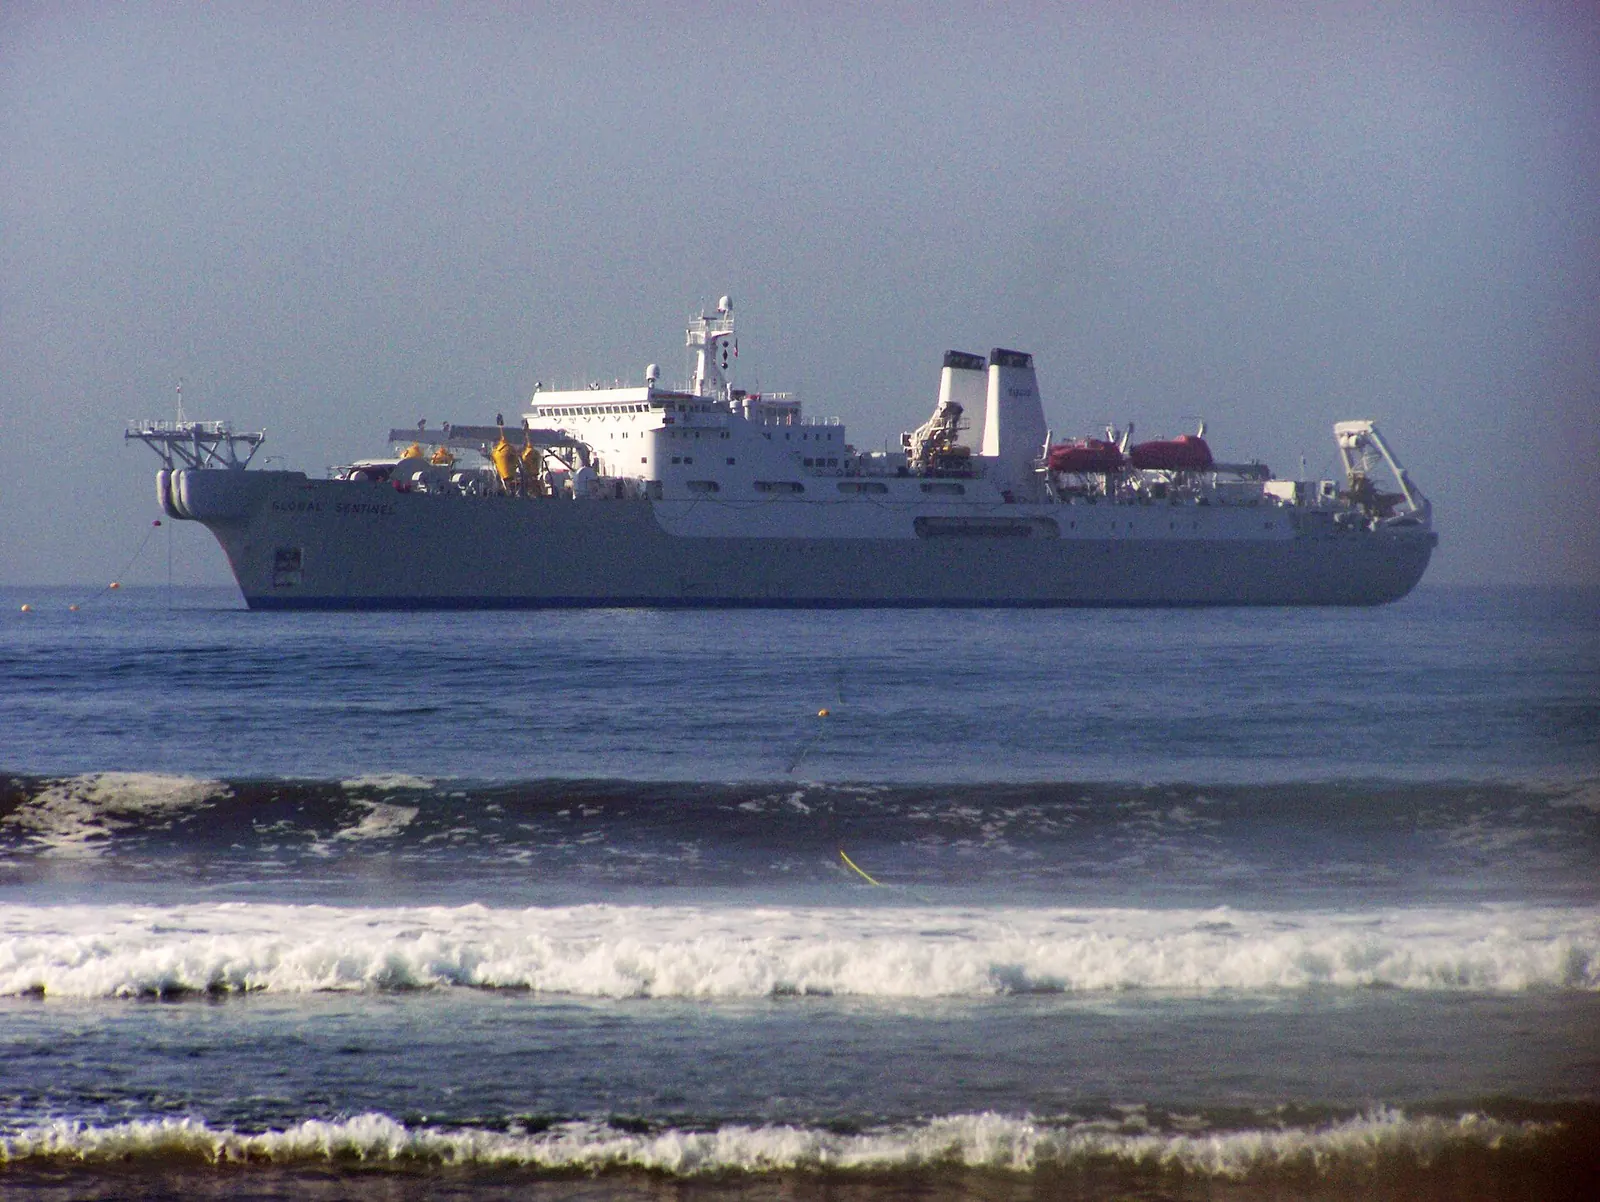
As reported by Defense News, the United Kingdom, Norway and the United States tracked and intercepted submarines belonging to GUGI, Russia's deep-sea research directorate, in spring 2026. The submarines were reported to have rehearsed a set-up capable of disabling cables without leaving a trace. The two cables in the target area connect Svalbard to the Norwegian mainland; each is about 1,400 kilometres long and descends to a depth of 2,700 metres.
The importance of these cables lies in the data they carry: they transmit data from SvalSat, the world's largest satellite ground station, which is also connected to the NASA network. No cable was damaged. The real message of the incident is that sabotage capability can be rehearsed in peacetime and that detection is possible only through joint allied maritime tracking. Cable security is no longer merely a telecoms matter but a question of the continuity of space and defence data.
Software layer: a shared exploit kit
According to Proofpoint's report of 9 September, the BlueMoon kit, first seen on 28 August, chains two Chrome V8 vulnerabilities with a Windows kernel vulnerability. The company identified four attacker clusters and classified three of them as China-aligned. TA412 targeted US civil society, mining and commodity trading firms; UNK_LateNight targeted US aviation companies; and UNK_QuietRacket targeted government and financial institutions in Indonesia and Singapore.
According to SecurityWeek, the kit circulated among different groups within a few days. This shows that the traditional patch cycle is not sufficient for defence: a vulnerability can be exploited by multiple groups before it is publicly disclosed. The commodity trading and mining firms on the target list indicate that cyber espionage functions as an extension of geo-economic competition.
Data layer: identity documents
As reported by The Record and Help Net Security, 153 million driving licence scans, 10 million identity cards and more than 3 million travel documents belonging to people in the US and Canada were stolen from the identity verification company IDScan. The data were put up for sale on 31 August on a Russia-linked illicit marketplace; the FBI has opened an investigation.
In the same week the US Treasury sanctioned Xinbi Guarantee, a Chinese-language illicit marketplace whose volume has exceeded 24 billion dollars since 2022. Read together, the two incidents reveal a cycle in which stolen identity data supplies raw material to the economy of fake account creation and fraud. The financial leg of this cycle lies in the scam centres of Southeast Asia, and the data leg in suppliers in the West.
Why actors choose these layers
What the three incidents have in common is that the attacker targets points where high impact can be achieved at low cost. The tracking resources needed to protect a cable in the deep sea are far greater than the resources needed to damage it. Exploiting a browser vulnerability is far faster than patching against it in every institution. Data stolen from an identity verification supplier weakens the security of millions of accounts in one stroke.
This asymmetry allows state-linked actors to exert pressure without entering open conflict. The link between identity data sold on Russia-linked illicit marketplaces and fraud networks in Southeast Asia shows that the criminal economy and state interests at times use the same infrastructure. On the defensive side, most of the cost falls on the private sector, infrastructure operators and insurers.
What to watch
Three indicators stand out. First, the frequency of official statements on suspicious maritime activity around cables and pipelines in northern Europe. Second, the speed at which institutions apply patches for the vulnerabilities used in the BlueMoon kit, and any new target regions. Third, reports of fraud waves making use of the IDScan data.
Verifiable quantitative data in this area are limited; most incidents come to light late and only partially. For this reason this report gives no estimate of the economic cost of the cyber incidents.
Probabilities
Scenarios
| Scenario | Probability | Trigger | Market impact |
|---|---|---|---|
| H1Continued grey-zone pressure | 60% | Cable rehearsals, espionage campaigns and data leaks continue without causing outages. | Costs accumulate in defence and compliance spending, with no service outages. |
| H2Physical outage | 25% | A data or energy cable in northern Europe is actually damaged. | Regional data traffic and satellite data transmission are disrupted for days. |
| H3Mass exploitation wave | 15% | BlueMoon-type vulnerabilities are used in a way that causes outages in finance or the power grid. | Service outages and data losses occur simultaneously in several countries. |
Module A
Constraints Matrix
STRUCTURAL AVG 4.0 · TACTICAL AVG 3.0Structural constraints dominate: the outcome is set more by these limits than by the actors' preferences.
Hard structural constraintspersistent · beyond the actors' will
Dependence on a few cables
4/5Data from the satellite ground station on Svalbard reaches the mainland via two subsea cables.
Supplier concentration
4/5The concentration of critical services such as identity verification in a few companies turns a single breach into a mass-impact event.
Tactical frictiontemporary · eases over time
Patch deployment lag weeks
4/5Zero-day vulnerabilities are shared among groups within a few days, while the corporate patch cycle takes weeks.
Maritime tracking capacity months
3/5Detecting deep-sea activity depends on the allies' joint tracking resources.
Investigation and disclosure time days
2/5Breaches become public days after they are detected; impact assessment is delayed.
Module B
Signal vs Noise
SIGNAL 67% · NOISE 33%
- SIGNAL
Sabotage capability is being rehearsed in peacetime
Submarines of Russia's deep-sea directorate were reported to have rehearsed, near the Svalbard cables, a set-up to disable cables without leaving a trace.
- SIGNAL
Exploit kits spread among groups within days
Proofpoint reported that the kit first seen on 28 August was used by four separate clusters.
- NOISE
Expectation that a single sanctions decision will end the fraud economy
Xinbi is the third major network targeted after Huione and Prince Group; earlier sanctions did not prevent new networks from forming.
Module C
Asset-Class and Positioning Implications
| Asset class | Exposure | Transmission channel | H1 | H2 | H3 | Expected | Conviction | Horizon | What to watch |
|---|---|---|---|---|---|---|---|---|---|
| Equities | Cyber security services sector | State-linked campaigns and compliance obligations | + | + | ++ | +1.15 | ●●● | 3–12 months | Frequency of critical infrastructure breach notifications |
| Freight & insurance | Cyber and subsea infrastructure insurance | Cable sabotage and mass breach risk | + | ++ | ++ | +1.40 | ●●● | 3–12 months | Statements on suspicious maritime activity in northern Europe |
| Volatility | European equity market volatility | Physical infrastructure outage | 0 | + | ++ | +0.55 | ●●● | 0–3 months | News of cable and grid outages |
Triggers
Thresholds to watch
| Indicator | Threshold | Today | What it means |
|---|---|---|---|
| Brent crude oil | > 120 | 130.80 | The zone where the market impact of infrastructure attacks grows during the energy shock. |
Sources
Sourcing and verification rules: methodology · Report an error: contact
Related reports
IICyber & Infrastructure·Analysis·Türkiye and Its Neighbourhood
The identity layer: 2.6 million attacks, a single CVSS 10.0 flaw and a breach affecting 10,218,802 people
Four records published on the same day show that the attack surface is shifting to the identity and access layer, and that defence diverges between three days and months according to institutional capacity.
Cyber & Critical Infrastructure Desk · 18 September 2026 · 9 min
IGeo-Economics·Analysis·Europe
The buffer is thin in two places at once: European storage at 68.5% while the Asian spot climbs to 30 dollars
Europe enters winter with storage 68.5% full while Asian spot LNG has climbed to 30 dollars. Two sides are competing for the same cargoes, and the outcome is measured not by price but by who withdraws from the market.
Energy & Shipping Desk · 18 September 2026 · 9 min
IIIConflict & Defence·Analysis·Europe
Ukraine–Russia: as momentum changes hands on the front, the war shifts to energy infrastructure
According to ISW data, the territory Ukraine recaptured in August exceeded Russian gains; even so, both sides are targeting each other's energy infrastructure more intensively.
Defence & Conflict Desk · 15 September 2026 · 8 min